How to Develop a Compliance Training Platform for Regulated Industries
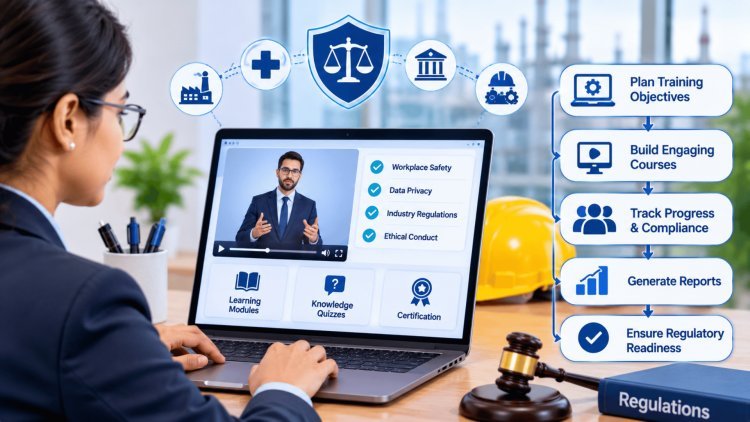
Building a compliance training platform for regulated industries is far more than creating an LMS with a progress bar. Industries governed by OSHA, FDA, state licensing boards, and quality-management frameworks require platforms that can prove training happened — with precision, by person, by role, by date, and by version. This presentation breaks down the core architectural and functional requirements your platform must address to withstand real audits, automate certification workflows, and produce defensible, regulator-ready evidence on demand.
The Real Problem: Audits Don't Care About "Completion"
Most organizations assume that if employees have watched a training video and clicked "complete," they are covered. Regulators disagree — and that gap is where compliance platforms most often fail. When OSHA inspectors, state licensing boards, FDA auditors, or quality review teams arrive, they do not ask for a completion percentage dashboard. They ask for training evidence by person, by course, by date, by location, and by role — and they expect it immediately.
The Spreadsheet Trap
The single most common compliance failure is an expired certification that nobody caught. This happens because tracking lives in disconnected spreadsheets, shared drives, or manual email workflows. When a certification silently lapses, there is no alert, no automatic reassignment, and no audit trail — until the regulator finds it first. At that point, the organization is already exposed.
Spreadsheets cannot enforce version control, cannot auto-expire records, and cannot bind a completion to the specific policy version the learner actually saw. They are fundamentally incompatible with the evidence standards of regulated industries.
The Difference Between Training and Compliance
If your platform cannot produce all of the above on demand, it is not a compliance platform — it is a content delivery system dressed up with a completion checkbox. The distinction matters enormously when regulators arrive unannounced.
The most dangerous compliance gap is not what employees don't know — it's what your platform can't prove they learned, when they learned it, and which version of the policy they were trained on.
Auditors do not measure completion. They measure evidence. A true compliance platform exists to create, preserve, and instantly produce that evidence at every stage of the training lifecycle.
Defensibility is the defining design principle for a regulated-industry compliance platform. Every architectural decision — from how completions are stored to how course content is versioned — must be evaluated through the lens of "could this record survive a regulatory audit?" The answer requires deliberate engineering, not retrofit features added after launch.
Every training completion must carry an immutable timestamp that records not just the date, but the precise time, the learner's authenticated identity, the device or session context, and the exact course version active at the moment of completion. This "current at the time" evidence model ensures that even if the course is updated six months later, the historical record reflects what the learner actually saw — which is what a regulator cares about. Platforms that simply overwrite records when content changes are fundamentally non-compliant with audit standards in industries like pharmaceuticals, healthcare, and financial services.
Bind every completion to a specific, immutable snapshot of the policy or course content. When regulations change and your course is updated, the system must maintain the prior version in an archived, read-only state — permanently linked to all completions that occurred under it. Exports provided to regulators should include the course version identifier, the content checksum or snapshot reference, and confirmation that the learner saw that version. This eliminates ambiguity during audits and prevents challenges to your training evidence. Formats should include PDF certificates, CSV exports, and structured JSON for integration with QMS or ERP systems.
For pharmaceutical, biotech, medical device, and clinical trial organizations, compliance platforms must align with 21 CFR Part 11 expectations — the FDA's framework for electronic records and electronic signatures. This means implementing audit trails that log every record creation, modification, and deletion; requiring electronic signatures that are unique to each user and cannot be reused or shared; and ensuring that system access controls prevent unauthorized record alteration. Even if your industry does not fall directly under Part 11, designing to this standard produces a platform robust enough for virtually any regulated context. It is a defensibility ceiling, not just a compliance floor.
Learn more about platform architecture best practices at Consac.dev.
Tamper-evident logs are not simply "logs that exist." They are append-only records that capture every system event — logins, completions, edits, exports, and administrative actions — in a way that makes retroactive alteration detectable. Cryptographic hashing, write-once storage tiers, and log integrity checks are standard engineering approaches. When an auditor reviews your logs, they should be able to confirm that no record has been silently edited since it was created. This architecture is non-negotiable for FDA, DEA, and Joint Commission environments.
Audit evidence must be filterable by organizational structure — not just by individual. Regulators frequently ask for all training records for the Chicago facility's maintenance team for Q3 or all OSHA 10-hour completions for field supervisors in the last 18 months. Your data model must support multi-dimensional filtering: by role, by department, by physical site, by regulatory requirement category, and by time period. Flat completion tables do not support this. A properly normalized data architecture with role-site-requirement mapping is essential from day one of platform design.
Slide into Defensibility: Audit-Ready Records + Version Control
Timestamp-Bound Completion Records
Course Version Control & Regulator-Proof Exports
FDA Part 11 & Electronic Signature Patterns
Tamper-Evident Logging Architecture
Role & Site-Specific Evidence Mapping
Manual compliance administration is not a scalable model for regulated industries. When an organization has hundreds of roles, dozens of sites, and regulatory requirements that change annually, human-managed assignment and tracking workflows inevitably produce gaps. The compliance engine of your platform must operate autonomously—assigning training, tracking expirations, triggering renewals, and surfacing dashboard evidence without requiring administrative intervention for each cycle.
Role-based assignment, proactive expiration alerts, automatic renewal, and tamper-evident audit coverage create a closed-loop compliance engine.
Automate the Compliance Engine:
Assign, Expire, Recertify, and ProveEliminate the “expired certification nobody caught” failure mode.
The final measure of a compliance training platform is not its content library or its user interface — it is how fast and how completely it can produce proof of compliance when a regulator, auditor, client, or licensing board asks for it. If generating an audit report takes more than a few minutes, your platform has already failed the compliance standard. Speed, completeness, and third-party verifiability are the three pillars of a launch-ready compliance outcome.
Build certificate verification into the platform from the start — not as a post-launch feature. Every certificate issued should carry a unique QR code or public verification link that allows any third party — a client, a general contractor, an insurance auditor, a licensing board — to confirm the certificate's authenticity without needing system access.
Wallet-style certificate sharing (Apple Wallet, Google Wallet) enables field workers to present proof of training on their phone in seconds. This eliminates the need for paper certificates, reduces administrative requests, and creates a self-service verification ecosystem that scales without additional staff.
Certificate records should be permanent and retrievable even after an employee departs, since regulators may audit historical records years after the fact. Explore how Consac.dev can help you architect a compliant verification system.
Your audit reporting system must be able to produce a complete, filtered, formatted evidence package in under five minutes — ideally in under two. Regulators arrive unannounced. Clients send compliance audits with 24-hour deadlines.
Your platform must support:
If your reporting module requires a data team, a business intelligence tool, or more than a few clicks, it is not audit-ready. Compliance reporting must be a first-class, self-service feature for non-technical compliance officers.
For further reading on platform scope and implementation patterns, review DigitalChalk's compliance training platform overview for real-world feature benchmarks, explore Koder.ai's guide to building compliance training web applications for technical architecture insights, and reference Belitsoft's compliance training management software breakdown for custom development considerations. Use these alongside your own regulatory research to build a platform that is not just functional — but genuinely defensible.
The standard for a compliant platform is not "did employees complete training?" — it is "can you prove, to any regulator, exactly what each employee was trained on, which version, when, and from which location?" Build to that standard from day one.
Launch-Ready Outcome: Regulator-Ready Reporting & Shareable Proof
Certificate Verification & Third-Party Sharing
Fast, Exportable Audit Reports
Further Reading & Architecture References
A launch-ready compliance platform succeeds when proof is instant, audit trails are immutable, certificates are independently verifiable, and every training record remains defensible years after completion.
What's Your Reaction?